
Artificial intelligence28 min read5490 wordsRedakcja dvnt
EU AI Act for business — duties, deadlines and fines after the 2026 changes
EU AI Act for business in Poland: what you must do if you use AI, when the rules apply, what the Polish AI act adds and what fines can reach.
The EU AI Act, the European regulation on artificial intelligence, is, for most small companies, not a compliance project but four concrete tasks. You do not use prohibited practices. You take measures that support the skills of people working with AI (Art. 4). You tell people they are dealing with AI, and you label deepfakes and some published texts (Art. 50). And if AI evaluates job candidates, employees or customers' creditworthiness, you prepare for the duties for high-risk systems, which start to apply on 2.12.2027.
Which of these duties applies to your company is decided by its role: provider of an AI system or deployer. It does not matter whether you pay for the tool. In Poland, from 28.10.2026, inspections and fines are in the hands of the Commission for the Development and Security of Artificial Intelligence (Komisja Rozwoju i Bezpieczeństwa Sztucznej Inteligencji, KRiBSI). From the same day you can ask it how the rules apply to your case, for PLN 150.
State of the law on 8.10.2026, after the amendment made by Regulation 2026/1744 of July 2026. This describes the rules and the official explanations of the European Commission and of the Polish data protection authority (UODO), not legal advice: for any borderline case decide with a lawyer.
The AI Act — what it is and what the July 2026 regulation changed
The AI Act is [Regulation (EU) 2024/1689](https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX:02024R1689-20260727), which applies directly in every member state of the Union, Poland included, without being transposed into national law. It entered into force on 1.08.2024, but at that point it did not yet require anything. Art. 113 spreads its application over stages from 2.02.2025 to 2.08.2028, and the general date of application is 2.08.2026. Texts that say "the AI Act has applied since 1.08.2024" confuse entry into force with application of the provisions.
On its page on the AI Act (updated 3 August 2026) the European Commission divides AI systems into four risk levels: unacceptable, high, transparency risk and minimal. The Commission puts "the vast majority of AI systems currently used in the EU" in the last group, for example AI-enabled video games and spam filters, and for them the AI Act introduces no rules. That is the Commission's assessment, not a measurement.
An AI system is, under Art. 3(1), a machine-based system that is designed to operate with varying levels of autonomy and that, for explicit or implicit objectives, infers, from the input it receives, how to generate outputs such as predictions, content, recommendations or decisions. In its non-binding guidelines on this definition (29.07.2025) the Commission notes that it is not possible to determine automatically which systems fall within it. Each tool is assessed separately.
The AI Act was amended in July 2026. Regulation (EU) 2026/1744 of 8.07.2026, named the "Digital Omnibus on AI" (the Commission calls it the AI Omnibus), was published on 24.07.2026 and entered into force on 27.07.2026. For a company that uses AI it changed five things:
- the obligations for high-risk systems in Annex III apply from 2.12.2027, and for Annex I from 2.08.2028, where before it was 2.08.2026 and 2.08.2027;
- Art. 4 on AI literacy received a new, milder wording;
- new prohibitions were added (Art. 5(1)(ba) and (bb)), applying from 2.12.2026;
- some of the simplifications provided for SMEs were extended to small mid-cap companies (Commission, 27.07.2026);
- providers of generative systems placed on the market before 2.08.2026 have until 2.12.2026 to technically mark content under Art. 50(2).
Texts from before 27.07.2026 that write about high risk "from August 2026" are therefore out of date. We show all the dates from 2024 to 2028 on one timeline in the guide AI in business; here we arrange them by whom they concern.
Provider or deployer — who your company is under the AI Act
Your duties depend on your role, and for a company that uses AI two matter: provider and deployer. Art. 3(3) defines a provider as a body that develops an AI system or "has an AI system developed" and places it on the market or puts it into service under its own name or trademark, "whether for payment or free of charge". A deployer is, under Art. 3(4), a body "using an AI system under its authority", except where the system is used in the course of a personal non-professional activity.
A company whose employees use ready-made tools, such as ChatGPT, Copilot, Gemini or a ready-made chat on a website, is therefore a deployer. That includes a sole trader (jednoosobowa działalność gospodarcza): Art. 2(10) excludes only deployers who are natural persons using AI systems "in the course of a purely personal non-professional activity", and the Polish Act on artificial intelligence systems likewise excludes in Art. 3(1)(1) only natural persons who use AI "solely for personal purposes not connected with business activity" (our translation). How a business plan of such a tool differs from a private one is compared in the article ChatGPT Business, Copilot or Gemini for business.
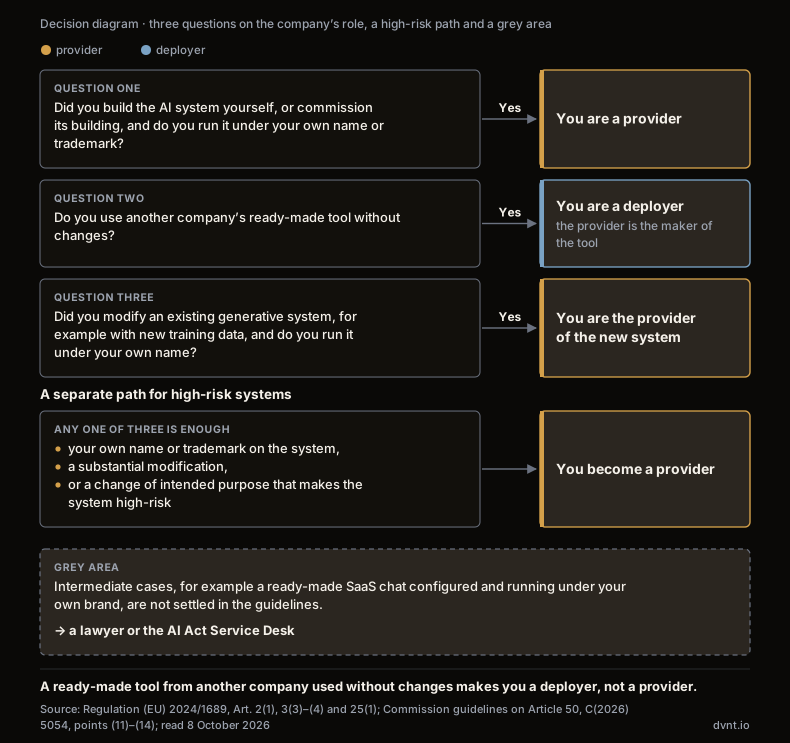
In its guidelines on Article 50 of 20.07.2026 the Commission gives three examples that settle the most common questions about role. The guidelines are not binding — an authoritative interpretation can ultimately only be given by the Court of Justice of the European Union — but they show how the Commission reads the rules:
- A ready-made tool used without changes. A company that provides a generative or interactive AI application (a chatbot, an image generator, an AI agent) under its own name or trademark to users who may use it without modification is a provider. You, as its customer, are a deployer, also when you build the tool into your own processes.
- A chat built in-house. A company that has developed a chat in-house and puts it into service for its own use under its own name is a provider.
- A modified generative system. A company that takes an existing generative system placed on the market by another provider, modifies it, for example with new training data, and puts it into service under its own name becomes the provider of the new system.
The guidelines also explain that a deployer's authority means taking responsibility for the decision to deploy the system and for the manner of its actual use, and does not necessarily require technical control. Employees acting under the company's instructions are not separate deployers. A company remains a deployer even if it involves third parties, such as contractors or freelancers, to operate the AI on its behalf. A company that merely commissions an advertising agency to produce an advertisement, without taking decisions about whether and how the agency uses AI, is not a deployer.
For high-risk systems the rule is written in the regulation itself. Art. 25(1) treats any distributor, importer, deployer or other third party as a provider if they put their name or trademark on a high-risk system, make a substantial modification to it, or modify its intended purpose so that the system becomes high-risk.
There is a case the guidelines do not settle: a ready-made SaaS chat that you configure yourself. Your own instructions, your own knowledge base from which the chat answers (that is how RAG works), a widget in your brand colours, but no training of the model. That is neither "use without modification" nor "modification with new training data". Settle such a case with a lawyer or, from 28.10.2026, ask KRiBSI for an individual opinion (see the section on the Polish act below).
What applies from when — duties by role
Some duties apply to every company from 2025, some only to providers, and the duties for high-risk systems start only in December 2027. The list below collects the dates from Art. 111 and 113 of the AI Act as amended by Regulation 2026/1744 and from Art. 127 of the Polish act.
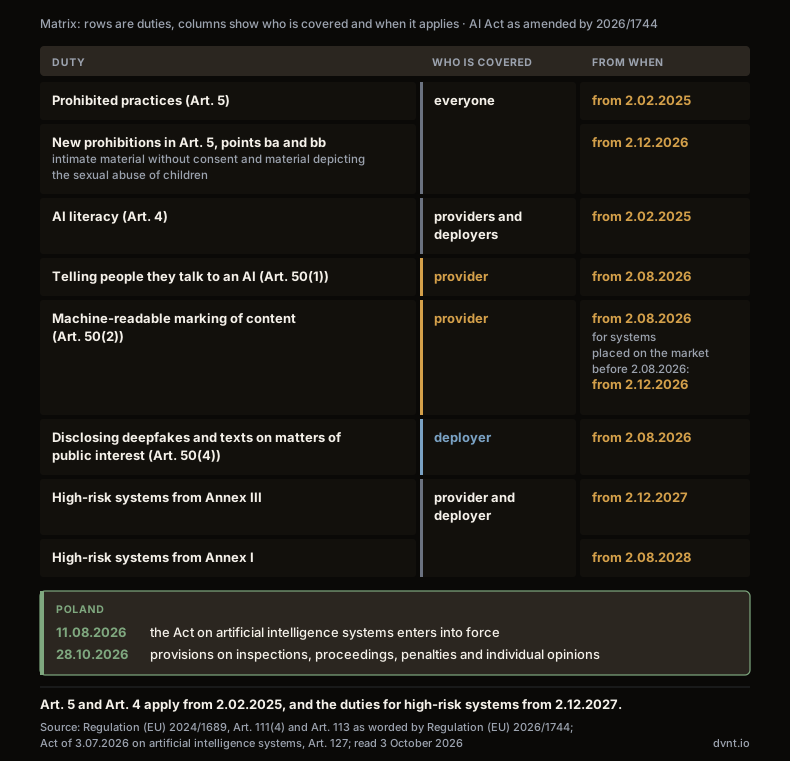
- Every company: the ban on the practices in Art. 5 and the duty in Art. 4 apply from 2.02.2025. The new prohibitions in letters (ba) and (bb) apply from 2.12.2026.
- Provider: telling people they are dealing with AI (Art. 50(1)) and marking content (para. 2) from 2.08.2026. Only the marking has an exception: for systems placed on the market before 2.08.2026 the deadline is 2.12.2026. Telling people they are dealing with AI has no such transitional period (Commission questions and answers on Art. 50, updated 24.07.2026).
- Deployer: disclosing deepfakes and some texts (Art. 50(4)) and informing about emotion recognition and biometric categorisation (para. 3) from 2.08.2026. The Art. 26 duties for high-risk systems from Annex III from 2.12.2027, from Annex I from 2.08.2028.
- Poland: the Act on artificial intelligence systems has been in force since 11.08.2026, and its provisions on inspections, proceedings, penalties and individual opinions apply from 28.10.2026.
According to the Commission, from 2.08.2026 the AI Office and the authorities of the member states are responsible for implementing, supervising and enforcing the AI Act. The AI Office holds enforcement powers over general-purpose AI models; in the Commission's Q&A on Art. 50, compliance "will mainly be enforced by national competent market surveillance authorities". In Poland that is KRiBSI, which gets its full set of supervisory tools only on 28.10.2026.
Prohibited practices — what no company may do
Art. 5 prohibits several uses of AI regardless of role and company size, and the ban has applied since 2.02.2025. In business terms:
- subliminal and manipulative techniques, and exploiting people's vulnerabilities (age, disability, social or economic situation), that lead to significant harm;
- social scoring;
- assessing the risk that a person will commit a crime solely on the basis of profiling;
- "untargeted scraping of facial images from the internet or CCTV footage";
- emotion recognition in the workplace and in education;
- biometric categorisation that infers race, political opinions, trade union membership, beliefs or sexual orientation;
- real-time remote biometric identification in public spaces for law enforcement, with narrow exceptions.
For an employer the key one is letter (f). It prohibits "the placing on the market, the putting into service for this specific purpose, or the use of AI systems to infer emotions of a natural person in the areas of workplace and education institutions, except where the use of the AI system is intended to be put in place or into the market for medical or safety reasons".
From 2.12.2026 two new prohibitions are added: AI systems that generate or manipulate realistic images, video or audio of an identifiable person's intimate parts or sexually explicit activities without that person's "freely-given, specific, informed, unambiguous and explicit consent" (letter ba), and material depicting the sexual abuse of children (letter bb). On its page the Commission counts them together as the ninth prohibited practice; in the regulation they are two new letters of Art. 5.
Breaching Art. 5 attracts the highest tier of fines: up to EUR 35 million or up to 7% of worldwide annual turnover (Art. 99(3)). On 4.02.2025 the Commission published guidelines on prohibited practices with explanations and examples; they are non-binding.
Art. 4 and AI literacy — what "supporting skills" means after the change
Art. 4 requires a company that uses AI to take measures supporting people's skills, not to guarantee a specific level. After the July 2026 amendment the provision reads: providers and deployers of AI systems "shall take measures to support the development of AI literacy of their staff and other persons dealing with the operation and use of AI systems on their behalf", taking into account their technical knowledge, experience, education and training and the context the systems are used in. It continues: "This obligation does not require providers or deployers to guarantee any specific level of AI literacy of any individual." The duty has applied since 2.02.2025.
In its questions and answers on AI literacy (updated 27.07.2026) the Commission answers the questions every small company asks:
- Does Art. 4 apply to a company whose employees use ChatGPT to write advertising copy or to translate? Yes. They should be informed about the specific risks, for example hallucination, that is a language model stating falsehood as fact. Where it comes from is explained in the article on large language models (LLMs).
- Is a certificate needed? No. Organisations can keep an internal record of trainings and other guiding initiatives.
- Do you have to appoint an "AI officer", like a data protection officer under the GDPR? No, no specific governance structure is mandated by Art. 4.
- Do you have to measure employees' knowledge? No, Art. 4 does not entail that.
The Commission also describes the minimum: ensure a general understanding of AI in the organisation, consider your role (provider or deployer), consider the risk of the systems you use, and base concrete actions on that analysis. It warns that in many cases simply relying on the systems' instructions for use or asking staff to read them might be ineffective. Supervision of Art. 4 belongs to national authorities, not the AI Office. For SMEs the Commission points to the European Digital Innovation Hubs (EDIHs) and to the AI Skills Academy, which has operated since 1.05.2026.
An internal AI use policy is our recommendation, not a statutory requirement. One page that records which tools the company uses, for what, what data must not be pasted into them and who answers questions can also serve as an internal record of the measures taken.
A separate and future duty concerns high-risk systems: from 2.12.2027 oversight of them must be assigned to people who have "the necessary competence, training and authority, as well as the necessary support" (Art. 26(2)).
Art. 50 — chat, agent, deepfake and texts: what a company must do
Art. 50 splits the duties: the provider is responsible for telling people they are dealing with AI and for technical marking of content, and the company that uses AI for disclosing deepfakes and certain texts. The duties apply from 2.08.2026.
Chat and agent: the information at the latest at the first interaction
Art. 50(1) obliges the provider to design the system so that the persons concerned are informed that they are interacting with an AI system, "unless this is obvious from the point of view of a natural person who is reasonably well-informed, observant and circumspect". Para. 5 adds that the information must be given "in a clear and distinguishable manner at the latest at the time of the first interaction or exposure" and must conform to the applicable accessibility requirements; who is bound by digital accessibility, and how, we cover in the article on WCAG.
According to the Commission's guidelines it is enough for a chat to start the conversation by mentioning that it is based on AI technology, or for an email generated by an AI agent to carry an AI label at the top. It is not enough to disclose it only in terms and conditions, URLs or documentation, to use unclear signals such as a generic reference to "assistant", a general statement like "Services on this website use AI", or a statement solely referring to the underlying technology such as "this system uses LLMs". The "obvious" exception should be interpreted restrictively, according to the Commission.
Three cases from the guidelines matter for customer service:
- simple automated responses that are not based on AI, such as a traditional out-of-office email, are outside the provision;
- a customer service representative who uses an AI assistance tool in the background to communicate is not covered by para. 1;
- if AI-generated responses are blended with human ones, you label the generated ones, unless they have been properly reviewed and sent by a person as the main interlocutor.
On agents the guidelines are explicit: AI agents are covered by Art. 50(1) if they are capable of interacting with the persons instructing them or with other natural persons in the execution of their tasks, such as making bookings, managing correspondence, negotiating or concluding contracts or executing purchases. They must disclose both their artificial nature and the person on whose behalf they are acting. More about agents is in the article AI agent in business, and about a chat in an online shop and who is responsible for this duty with a ready-made bot, in the text on ecommerce customer service. Where to plan this disclosure when building an agent, alongside approvals and limits, is covered in the guide on how to build an AI agent.
Marking content — a duty of the tool provider
Art. 50(2) requires providers of generative systems to ensure that outputs "are marked in a machine-readable format and detectable as artificially generated or manipulated". That is the work of the generator's maker, not of the company that uses it. The exception covers systems that perform an assistive function for standard editing.
Deepfakes and texts — a duty of your company
The rules contain no duty to label every piece of content created with the help of AI. Art. 50(4) concerns the deployer, that is you, and covers two things. If you publish images, audio or video that are a deepfake, you disclose that they have been artificially generated or manipulated. A deepfake is, under Art. 3(60), content that resembles existing persons, objects, places, entities or events and would falsely appear to a person to be authentic or truthful.
That is why the guidelines give an example from selling. An AI-generated image of a product in an advertisement or on packaging that can affect the audience's perception and mislead as to the actual product appearance, characteristics or use, for example by making it appear more appealing or of better quality than in real life, is a deepfake. A real product, such as a car, shown against an AI-generated background is not, as long as the advertisement is not likely to mislead about the product itself. Colour correction, background extension or re-scaling of product images is likely to have only a minor impact, according to the Commission. Where to legally get photographs for a website is covered in the text on images for a company website.
You disclose a text only if you publish it to inform the public on matters of public interest. The Commission excludes advertising and product descriptions, unless they contain claims about, for example, health, consumer safety or sustainability, and also private correspondence and internal texts. As an example of a text in scope it gives a corporate report published on a listed company's website containing investor information.
A text on matters of public interest does not need labelling if two conditions are met at once. First, a person with relevant knowledge has reviewed its substance; fact-checking is the minimum according to the Commission, and spell-checking or grammar correction is not enough. Substantial changes made by AI after sign-off void that review. Second, a person, a company or a function (for example the editor-in-chief) bears editorial responsibility, and their identity and contact details are publicly available in an easily findable place.
Content generated before 2.08.2026 does not have to be labelled retroactively, unless you publish it on or after that date. The Commission and the AI Board have confirmed the code of practice on transparency of AI-generated content as an adequate voluntary tool to demonstrate compliance; according to the Commission's press release of 31.07.2026 more than 180 organisations signed it. To label content you may voluntarily use the icons created by the EU. Copyright in AI-generated content is a separate topic, outside the AI Act; we touch on it in the article on logo design.
High risk: when it concerns a small company and what applies from 2.12.2027
A system becomes high-risk through its use, and for a typical small company the first such use is recruitment. High risk is associated with face recognition, but in a small company it is usually the HR function that meets it. Annex III point 4(a) covers "AI systems intended to be used for the recruitment or selection of natural persons, in particular to place targeted job advertisements, to analyse and filter job applications, and to evaluate candidates". On its page on the AI Act the Commission gives CV-sorting software for recruitment as an example: a tool that screens applications itself and ranks candidates.
Letter (b) of the same point covers systems for decisions on terms of employment, promotion and termination, for allocating tasks based on behaviour or personal traits, and for monitoring and evaluating the performance of workers. The other areas of Annex III that can concern SMEs are:
- evaluating the creditworthiness of natural persons or establishing their credit score, except for detecting financial fraud (point 5(b));
- risk assessment and pricing in life and health insurance (point 5(c));
- education and vocational training: access, evaluating learning outcomes, monitoring during tests (point 3);
- biometrics, including emotion recognition (point 1).
The exception in Art. 6(3): an Annex III system is not high-risk if it does not materially influence the outcome of decision-making, because it performs a narrow procedural task, improves the result of a previously completed human activity, detects patterns without replacing human assessment, or performs a preparatory task. The exception does not work when the system profiles people: such a system "shall always be considered to be high-risk". Check a tool that evaluates candidates on their characteristics from exactly that angle. We know the Commission's guidelines on classification only from the draft consulted until 23.07.2026.
From 2.12.2027 a company that uses a high-risk system from Annex III must, under Art. 26:
- use it in accordance with the provider's instructions for use;
- assign human oversight to people who have the necessary competence, training and authority, as well as the necessary support (para. 2);
- ensure that input data is relevant, to the extent it controls it;
- monitor the operation of the system and, where it considers that the system poses a risk, without undue delay inform the provider or distributor and the relevant market surveillance authority, and suspend use of the system (para. 5);
- keep the logs for at least six months;
- before using the system at the workplace, inform workers' representatives and the affected workers (para. 7);
- inform natural persons who are subject to decisions the system helps to take that it is used on them (para. 11);
- use the information from the provider in the data protection impact assessment under the GDPR (para. 9).
There is an exception for systems placed on the market or put into service before that date: the regulation applies to them only if they are subject to significant changes in their designs later (Art. 111(2); systems intended for public authorities have a separate deadline, 2.08.2030). Whether an update of a tool you buy by subscription is such a change, settle with a lawyer.
A fundamental rights impact assessment (Art. 27) does not concern a typical SME: it covers public bodies, private entities providing public services, and private companies that use systems for credit scoring or for life and health insurance. The duties of providers of high-risk systems, that is conformity assessment, documentation and registration, are a separate and heavier package, which the July 2026 amendment partly simplified for SMEs and small mid-cap companies.
On 16.07.2026 the President of the Personal Data Protection Office (UODO) noted that he receives "more and more signals about AI-based tools being used in recruitment processes" (our translation). A chat on a website and an AI agent are not high-risk systems by their nature: as with recruitment, the task you use them for decides.
Fines — what an SME actually risks
The AI Act has three tiers of fines, and for SMEs the lower of the two amounts counts: the amount in euros or the percentage of turnover. Art. 99 provides for:
- up to EUR 35 million or up to 7% of total worldwide annual turnover for the preceding financial year for prohibited practices (para. 3);
- up to EUR 15 million or up to 3% for breaches of, among others, deployers' obligations under Art. 26 and transparency obligations under Art. 50 (para. 4);
- up to EUR 7.5 million or up to 1% for supplying incorrect, incomplete or misleading information to authorities (para. 5).
For large companies the higher amount applies. For SMEs, including start-ups, each fine "shall be up to the percentages or amount referred to in paragraphs 3, 4 and 5, whichever thereof is lower" (para. 6). After the July 2026 amendment the same rule applies to small mid-cap companies, but only for the thresholds in paragraphs 4 and 5 (para. 6a).
In Poland the euro amounts are converted at the National Bank of Poland (NBP) average rate of 28 January of the given year (Art. 104(4) of the Polish act), not at the current rate.
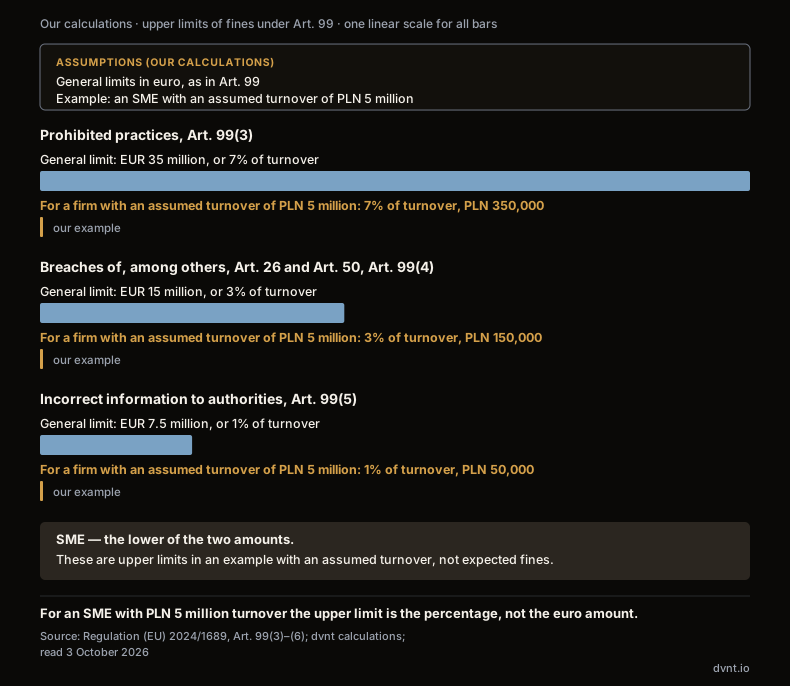
The calculation (our arithmetic): for an SME with an assumed annual turnover of PLN 5 million the percentages give PLN 350,000 (7%), PLN 150,000 (3%) and PLN 50,000 (1%). Each is far below the euro caps, so the percentages are the upper limits under Art. 99(6). These are upper limits in an example with an assumed turnover, not expected fines.
The actual size of a fine is set by the authority. Art. 99(7) lists the circumstances it takes into account, including the size, annual turnover and market share of the company and its degree of cooperation, and para. 1 requires the interests and economic viability of SMEs to be taken into account. The Polish act adds its own rules. KRiBSI may reduce a fine by 10–50% if, within three months of being served the decision imposing it, you carry out the actions it set out earlier in a warning, and the breach did not lead to death or serious harm to health (Art. 107(1)). A settlement on extraordinary mitigation of the sanction is possible (Chapter 5). You appeal against a decision to the Regional Court in Warsaw — the court of competition and consumer protection (Art. 109). Obstructing or preventing an inspection is an offence punishable by restriction of liberty or a fine (Art. 112).
Art. 4 is not on the list of breaches in Art. 99(4). In Poland proceedings and fines are possible only from 28.10.2026.
The Polish Act on artificial intelligence systems and KRiBSI
The [Act of 3 July 2026 on artificial intelligence systems](https://isap.sejm.gov.pl/isap.nsf/DocDetails.xsp?id=WDU20260001003) (Journal of Laws 2026, item 1003) mainly sets out who enforces the AI Act in Poland, and how. Among other things, it governs the organisation of market surveillance of AI systems, proceedings for infringements and the rules for imposing fines (Art. 1). It was published on 27.07.2026 and entered into force on 11.08.2026. The chapters on inspections, proceedings, settlements and penalties, and the provisions on individual opinions, apply from 28.10.2026 (Art. 127). The act has no official English text; the quotations here are our translation.
The market surveillance authority is the Commission for the Development and Security of Artificial Intelligence, KRiBSI (Art. 5); it is also Poland's entry on the Commission's list of market surveillance authorities under the AI Act (last updated 7 September 2026). It is made up of a chair, two deputies and four members nominated by the President of UOKiK (the competition and consumer protection office), the Polish Financial Supervision Authority (KNF), the National Broadcasting Council (KRRiT) and the President of UKE (the electronic communications office) (Art. 19). KRiBSI cooperates with, among others, the President of UODO. The body is already up and running: on 18.09.2026 the Sejm appointed Pamela Krzypkowska as its chair, and on 24.09.2026 the Senate consented (M.P. 2026 item 945 and item 946).
Inspections. KRiBSI inspects businesses under the rules of the Entrepreneurs' Law (Prawo przedsiębiorców). An inspection may start no earlier than 7 days after the notice is served (Art. 49(2)). As a rule it is carried out remotely; on site only on the basis of an order, where there is a reasonable suspicion of harm to people's life, health, safety or fundamental rights (Art. 49(3)–(4)).
A warning before a fine. Proceedings are opened ex officio, including after a complaint. Where it reasonably suspects an infringement, KRiBSI may issue a warning that sets out remedial actions; within 21 days you tell it you have carried them out (Art. 61). A decision orders the effects of an infringement to be removed within 14 days, and the authority takes compliance with that order into account when setting a fine (Art. 62).
The individual opinion is the most practical tool in the act. An application may be filed by a company covered by the AI Act, but also by one that is only planning activities that will bring it within its scope (Art. 9). The question may concern an actual situation or a future event. The fee is PLN 150 (Art. 11). KRiBSI has 30 days to answer, and 60 days in particularly complex cases. If it does not answer in time, it is deemed to have issued an opinion in line with the position you set out in your application (Art. 12(3)). The opinion binds KRiBSI and other state authorities in your case (Art. 13), and following it cannot harm you (Art. 15(5)). The same company may file another application no earlier than 30 days later. Opinions will be available from 28.10.2026; they suit exactly the intermediate cases, such as a SaaS chat running under your own brand.
Until then — and alongside KRiBSI — the Commission's AI Act Service Desk offers a compliance checker, a tool that assists in evaluating whether AI systems and general-purpose AI models meet the requirements, and a team of experts to whom you can submit questions, "including in your own language". We found no statement on whether its answers are binding, so we do not call them binding.
The AI Act and GDPR — two lists, not one
The AI Act does not replace the GDPR: if an AI tool processes personal data, both apply at once. Art. 2(7) of the regulation provides that it does not affect Regulation (EU) 2016/679, and the Ministry of Digital Affairs (3.08.2026) says plainly that the rules "should be applied in parallel" (our translation).
For the GDPR part, the simplest tool comes from UODO. Its GDPR checklist for SMEs deploying AI of 6.08.2026 is meant for companies that use ready-made tools without training models. According to UODO it takes about 30 minutes to fill in, and more than three "NO" answers mean you should consult a specialist before using the tool any further. Keep the completed checklist: in an inspection or after a complaint it shows that the company checked the matter before deployment. UODO stresses that the checklist is not a binding interpretation of the law and does not settle GDPR compliance.
The core of the checklist fits in one sentence from UODO: before a tool is used on customer or employee data, you need a contract with the provider, an established legal basis for processing, information for the people whose data goes into the tool, and knowledge of where the data is stored. According to UODO a data processing agreement (Art. 28 GDPR) is needed for most cloud AI services. If a tool is meant to take decisions about people on its own, without an employee, change the way you use it or give it up. The SME version is not enough when the company trains a model, when the tool affects people's legal situation (recruitment, appraisal of employees, scoring of customers), for sensitive data and children's data, or when data leaves the European Economic Area.
The European Data Protection Board says in its Opinion 28/2024 (17.12.2024) that supervisory authorities should take into account whether the controller deploying a model conducted an appropriate assessment, as part of its accountability obligations, to ascertain that the model was not developed by unlawfully processing personal data. What must go into the privacy notice on a website we describe in the text on GDPR on a website, and how to find out where company data lives in the piece on company data security.
The AI Act in a small company — a checklist
Ten points organise what we described above; it is our list, not an official one, and it does not replace a legal assessment.
- List the AI tools and uses in the company: what you use, who and for what, on what data.
- Determine the role for each tool: provider or deployer (the section on roles and the diagram).
- Check that no use is prohibited, especially emotion recognition of employees (Art. 5).
- Take the Art. 4 measures matched to roles and risk and record them internally; no certificate is needed.
- Chat and agent: if you are the provider, tell people it is an AI in the first message, also in emails sent by an agent, together with the person on whose behalf it acts (Art. 50(1) and (5)); if you use a ready-made tool, check that the provider does it.
- Deepfakes and public texts: labelling or, for texts, substantive human review and openly assigned editorial responsibility (Art. 50(4)).
- Recruitment, appraisal of employees, scoring: a plan to adapt by 2.12.2027 (Art. 26).
- Contracts with providers: a data processing agreement under the GDPR, and if you yourself are the provider of a high-risk system, also the written agreement with the supplier of tools or models mentioned in Art. 25(4).
- The UODO checklist for every use on personal data; keep the completed one.
- In doubt: a lawyer, the Commission's AI Act Service Desk with its Compliance Checker and contact in your own language, and from 28.10.2026 an individual opinion from KRiBSI.
Frequently asked questions about the AI Act
Does the AI Act apply to a small company that only uses ChatGPT?
Yes. A company whose employees use ChatGPT at work is a deployer under the AI Act. Art. 4 has applied to it since 2 February 2025: it has to take measures supporting its staff's AI literacy, for example knowledge of hallucinations, as the European Commission answers in its questions and answers on AI literacy. Under Art. 50(4) it must disclose generated deepfakes and texts published to inform the public on matters of public interest, if it publishes any. Only purely personal use unconnected with business is excluded, so the AI Act also covers a sole trader.
Do I have to label AI-generated texts and images on my company website?
Not all of them. According to the European Commission's guidelines of 20 July 2026, advertisements and product descriptions generated by AI are not subject to the text-labelling duty unless they contain claims about, for example, health, consumer safety or sustainability. You label a deepfake, and a generated product photo that shows the product better than it is can be one. Texts on matters of public interest are labelled unless a person has reviewed them substantively and editorial responsibility is public. The guidelines are not binding.
Do employees need a certificate from AI training?
No. The European Commission says in its questions and answers on AI literacy that no certificate is needed and that an internal record of trainings or other initiatives is enough. Art. 4 in its July 2026 wording does not require a specific level of skills, does not require measuring employees' knowledge and does not require appointing a person responsible for AI.
Who enforces the AI Act in Poland and since when can it impose fines?
The market surveillance authority is the Commission for the Development and Security of Artificial Intelligence (KRiBSI), set up by the Act of 3 July 2026 on artificial intelligence systems. The act has been in force since 11 August 2026, but its provisions on inspections, proceedings and penalties apply from 28 October 2026. KRiBSI is chaired by Pamela Krzypkowska, appointed by the Sejm on 18 September 2026 with the Senate's consent of 24 September 2026. The AI Office at the European Commission holds enforcement powers mainly over general-purpose AI models; according to the Commission, the Art. 50 duties are enforced mainly by national authorities.
What fines can SMEs face under the AI Act?
Art. 99 provides for up to EUR 35 million or 7% of worldwide annual turnover for prohibited practices, up to EUR 15 million or 3% for breaches of, among others, Art. 26 and Art. 50, and up to EUR 7.5 million or 1% for incorrect or misleading information to authorities. For SMEs the lower of the two amounts counts. In Poland the euro amounts are converted at the NBP rate of 28 January. In our example of a company with a turnover of PLN 5 million the upper limits are PLN 350,000, PLN 150,000 and PLN 50,000; that is a maximum, not an expected fine.
Can I ask an authority how the AI Act applies to my company?
Yes, from 28 October 2026. An application to KRiBSI for an individual opinion costs PLN 150 and may also concern planned activities. KRiBSI answers within 30 days, or 60 days in particularly complex cases; no answer in time means an opinion in line with your position. The opinion binds state authorities in your case. You can already use the European Commission's AI Act Service Desk, which according to the Commission you can contact in your own language.
Related articles
Artificial intelligence
ChatGPT Business, Copilot or Gemini for business — plans, prices and data
ChatGPT Business, Copilot or Gemini for a Polish company: what a business plan changes, price per user in PLN, the GDPR processing agreement and your suite.
Artificial intelligence
Large language model (LLM) — what it is and what a business needs to know
An LLM writes text token by token. Why it errs, what a context window is, why Polish text costs more tokens, and the Polish models Bielik and PLLuM.
Artificial intelligence
AI agent in business — what it is and when it makes sense
An AI agent is a language model that chooses its own steps and tools. When it makes sense in a company, what it costs and what the AI Act and Polish law say.
Artificial intelligence
RAG AI — how AI answers from your company's own documents
RAG AI lets a language model answer from your company documents. How it works, what breaks the answers, what it costs in PLN and how to start safely.
Artificial intelligence
AI in business — where to start, what it costs and what the law says
AI in business without the hype: how many Polish firms use it, when an assistant is enough, what it costs and what the AI Act and Polish act require.
Artificial intelligence
AI hallucinations — why AI makes things up and how a business can catch it
AI hallucinations are confident but false answers from a language model. Why they happen, where they cost a business in Poland and how a process catches them.
Where would AI really pay off for you?
Tell us which tasks take up most of your time today. We will check whether an off-the-shelf assistant is enough or whether you need an implementation on your own data. If ChatGPT on a business plan will do, we will say so plainly.